Technical Intelligence. Legal Precision. Rapid Action.
Modern financial cybercrime operates across borders, anonymizing mixers, and decentralized networks. Veritas Cyber Recovery deploys specialized investigative methodologies tailored to each threat vector. Specialized blockchain forensics and legal investigative methodologies tailored to each fraud vector.
Targeted Solutions For Digital Asset Recovery.
Every fraud pattern leaves forensic breadcrumbs. Discover how our specialized teams unravel complex schemes to locate and recover your funds. Specialized teams unraveling complex schemes to locate and repatriate your funds.
Cryptocurrency & Web3 Asset Tracing
Blockchains are immutable ledgers of evidence. Using state-of-the-art heuristic clustering, we follow funds across Bitcoin (UTXO), Ethereum, Tron (TRC-20 USDT), Solana, and cross-chain bridges. We de-anonymize transactions passing through obfuscation mixers (Tornado, Sinbad, Wasabi) until they reach KYC-regulated Centralized Exchanges (CEXs).
Investment Fraud & Bogus Brokerage Dissolution
Unregulated offshore brokerages use simulated interfaces to display fictitious profits while restricting withdrawals behind fake "margin fees" and "tax clearance" demands. We audit trading server logs, unmask corporate shell entities in St. Vincent, Seychelles, Cyprus, and the Marshall Islands, and seize payment merchant accounts.
Corporate Wire Fraud & SWIFT Interception
When high-value bank wires or commercial real estate transactions are hijacked via executive impersonation or vendor email compromise, minutes matter. We collaborate with international financial institutions, generating SWIFT MT199 and MT299 recall urgencies and placing holding liens on recipient correspondent banks.
Romance & "Pig-Butchering" (Sha Zhu Pan) Infiltration
Organized transnational syndicates build trust over months before directing victims into fraudulent crypto investment platforms. We treat these cases with deep empathy and uncompromising forensic rigor—identifying the domestic money mule network, tracing crypto ATM conversions, and compiling law enforcement briefs.
Court-Admissible Evidence Dossiers
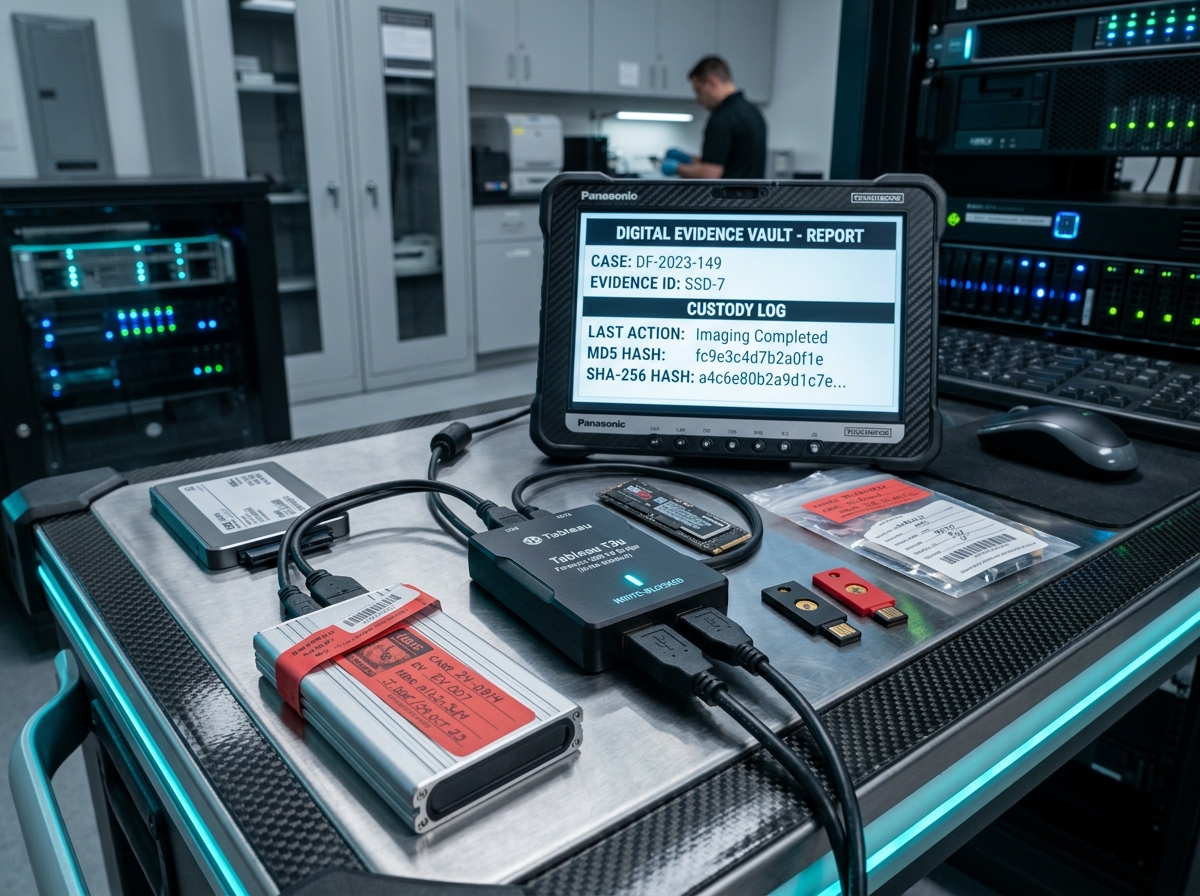
Raw screenshots are regularly dismissed in court. Our digital evidence vault adheres strictly to ISO/IEC 27037 standards, utilizing hardware write-blockers, cryptographic SHA-256 hashing, and unbroken chain of custody records accepted by judicial bodies worldwide.
Forensic Requirements by Incident Class.
Understanding the technical prerequisites helps expedite your recovery timeline.
| Fraud Category | Primary Evidence Needed | First Forensic Step | Intervention Window | Typical Resolution |
|---|---|---|---|---|
| Crypto / DeFi | Transaction Hashes (TXIDs), Deposit Addresses | Cluster mapping & CEX wallet tagging | < 72 Hours Optimal | 14 – 35 Days |
| Fake Broker / Forex | Trading URLs, Deposit Slips, Chat Transcripts | Domain WHOIS audit & Acquirer notice | < 30 Days | 30 – 60 Days |
| Bank Wire / BEC | SWIFT MT103, Email RFC822 Headers | Emergency MT199 Recall & Correspondent Lien | < 48 Hours Critical | 7 – 21 Days |
| Romance / Pig Butchering | Chat logs, Platform links, Wallet transfers | Mule network isolation & Law enforcement pack | < 60 Days | 30 – 75 Days |
Begin Your Evidence-Led Recovery Case.
Our intake analysts review your documentation under non-disclosure to evaluate feasibility before you commit to forensic investigation.
Submit Incident Details Now